
Security reviews and contacting MockFlow
How to send a security questionnaire, request compliance reports, report a vulnerability and check MockFlow's service status.
Before a company adopts MockFlow, its security or procurement team often needs answers about how MockFlow protects data. The MockFlow team is happy to help with security reviews, questionnaires and procurement, and to hear about any security issue you find.
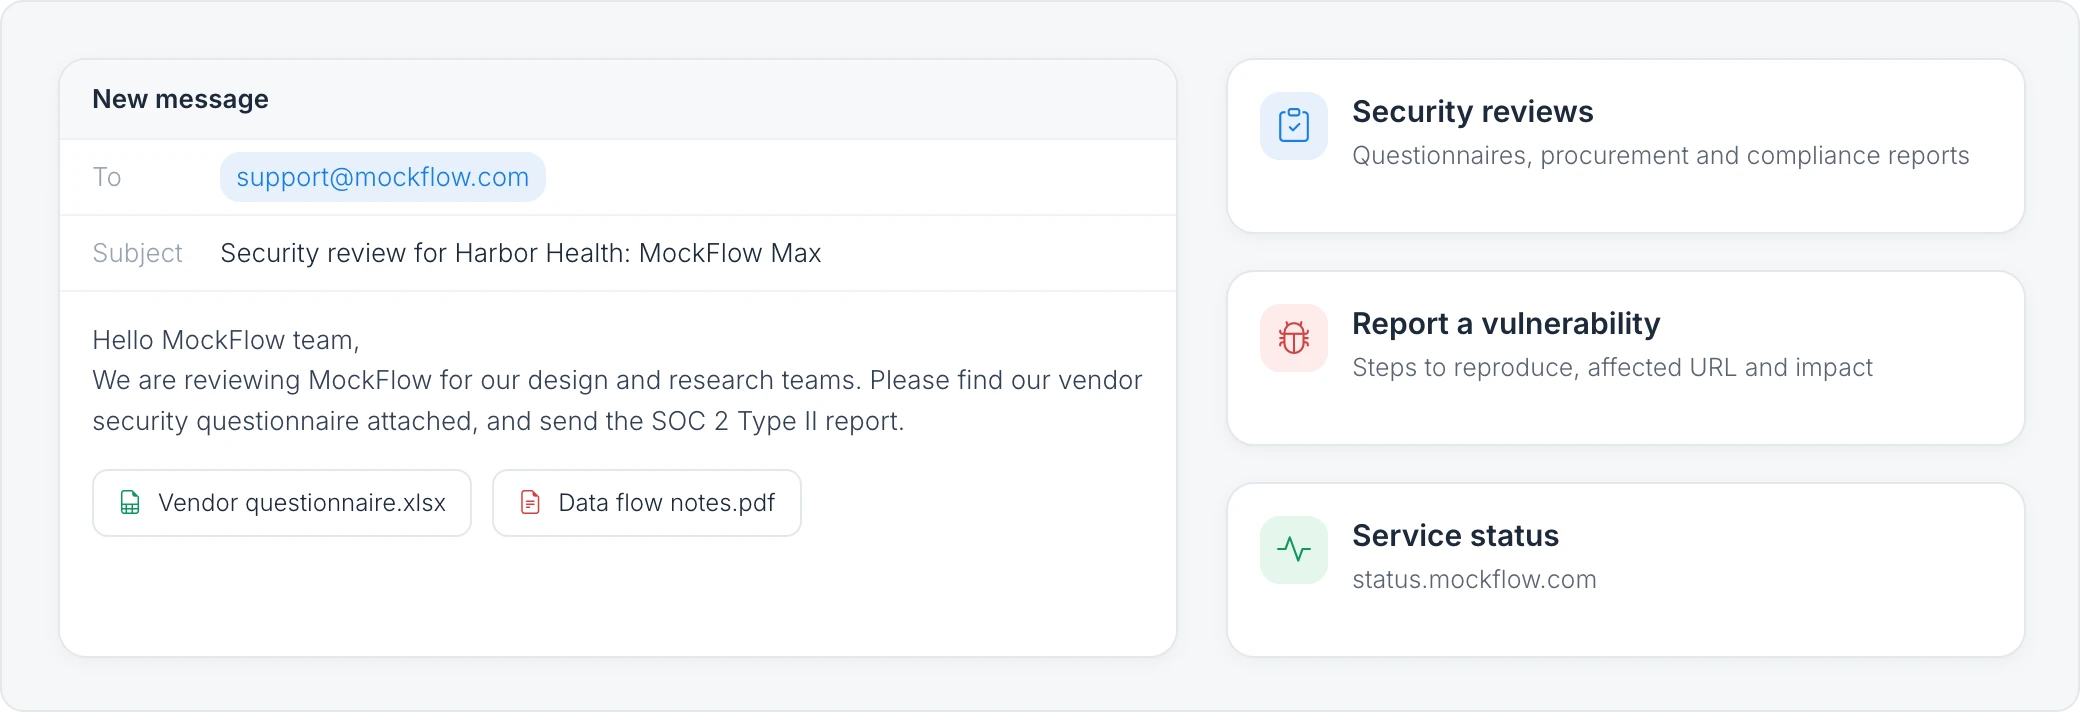
Send a security questionnaire
Email support@mockflow.com with your company name, the plan you are evaluating and your questionnaire. Many answers are already in this section:
Security at MockFlow for infrastructure and secure development
Where your data is stored and how it is backed up for hosting and backups
How MockFlow encrypts your data for encryption
Security controls for team admins for SSO, 2FA, SCIM and roles
Request compliance reports
MockFlow was previously certified for SOC 2 Type II and ISO 27001, and a new SOC 2 Type II audit is under way. To request the earlier reports, email support@mockflow.com. See SOC 2 and ISO 27001 compliance.
Report a security vulnerability
If you find a security issue in MockFlow, email support@mockflow.com with:
The page or feature affected, such as the board link or the URL
Steps to reproduce the issue
What an attacker could do with it
Please give MockFlow time to fix the issue before sharing it publicly, and do not access, change or delete other people's data while testing.
Check service status
See the current status of MockFlow and any ongoing incidents at status.mockflow.com.